Tag Archives: microsoft

Microsoft’s AI assisted blog posts

Last week I wrote about Microsoft’s Reactor framework, a React-inspired C# framework for WinUI, using an official blog post by principal software developer engineer Alexandre Zollinger Chohfi as one of the sources.

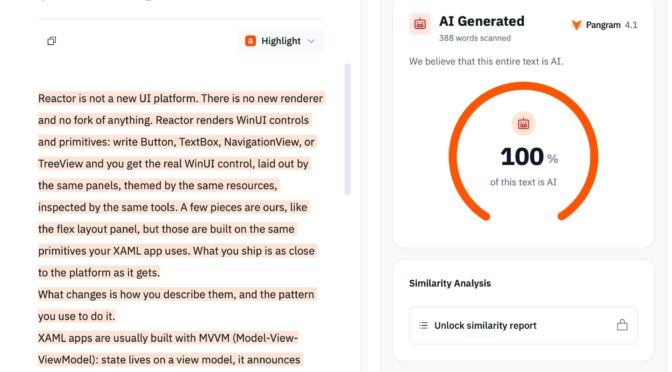
But was the post really by Chohfi? As I read it, I was pretty sure that it was AI-generated. Pangram, an AI detection engine, agrees with me (note this is based only on the first 388 words).
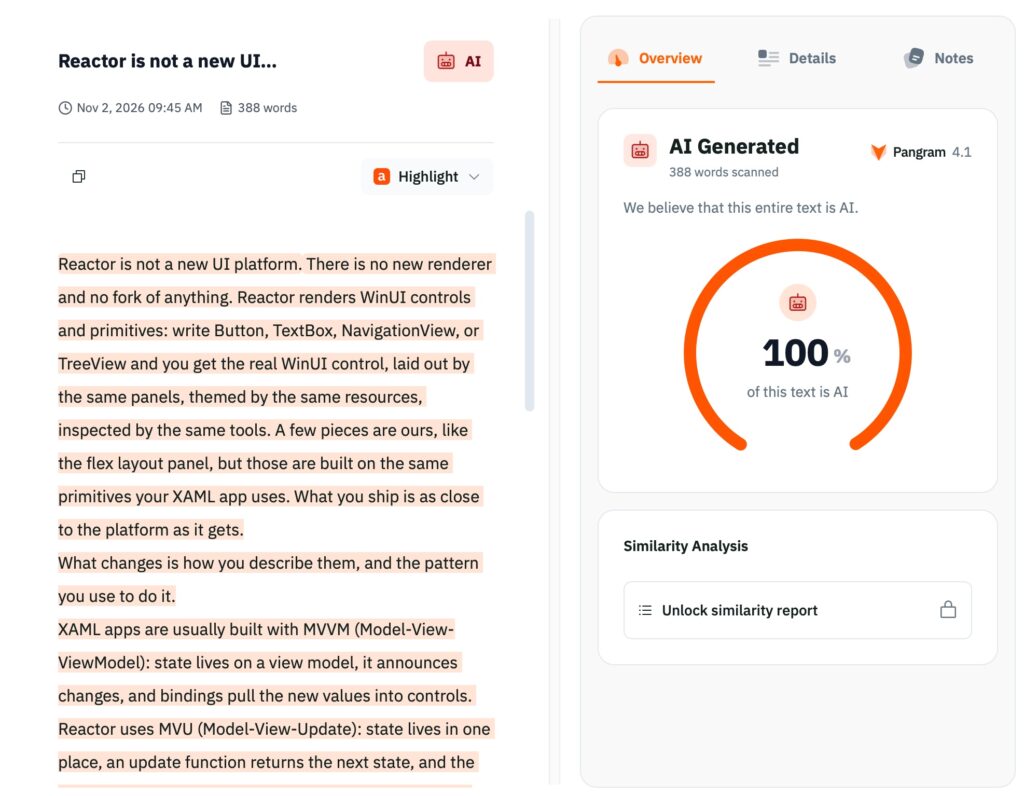
Pangram is confident that the Microsoft post was AI-generated

I see a lot of AI-generated text, for example in my own (light) use of AI coding tools, in code comments and issues on GitHub, in forum posts, and in emails. There are many indicators, though it is hard to pick them out in what is a subjective impression. A phrase like “new controls and patterns get tried here first, and the ones that prove themselves are candidates to land in WinUI itself” just sounds like AI to me. It is not bad writing, but why “to land in WinUI”? Why not, “for WinUI”? It is breezy for the sake of it, and does not come over as something a human would write.

Questions that interest me are first, does it matter, and second, should it be acknowledged, in the same way that Facebook now marks some posts as “AI content” (though I’m not sure how accurate it is).

For me it does matter. In particular, the AI-generated or AI-assisted content removes the personality of the human author who oversaw it, even if the text ends up being better written by some metrics. I would rather have worse English but with a sense of who the author is and what they think and feel about their subject matter.

There is also the possibility of AI-generated mistakes, though if the text is properly reviewed this should not be a concern. With a journalist hat on, I think it is OK to quote such text as if it were written by the author to whom it is attributed. That person is taking responsibility for the text by putting their name to it.

Should it be acknowledged? I would prefer this, but acknowledge that it is difficult. If someone fixed spelling or changed punctuation because of squiggly lines in Microsoft Word, is that AI assistance? Not really. It is hard to determine at what point the line is crossed.

I suspect that part of the reason for using AI assistance is that people lack confidence in their own writing, particularly if it is not in their native language. That is understandable, but from my perspective, I want to hear from the author, not a bland AI-generated post based on the author’s notes, or worse, an author sitting back and letting AI do all the research and the write-up as well.

WinUI Reactor: yet another way to code for the Windows desktop

Microsoft principal software developer engineer Alexandre Chohfi has posted about WinUI Reactor, an experimental framework for building WinUI applications using C# and a reactive pattern. The rationale for Reactor is two-fold:

  1. The popularity of React for web applications, and other reactive frameworks like SwiftUI and Jetpack Compose, makes using XAML for the user interface a barrier to adoption.
  2. Writing the user interface in plain C# is “easy for coding agents to read, write and check, so we now design for agents as well as people,” said Chohfi.

Note that Reactor is not a new platform, it is another way to code for WinUI, the existing platform which is supposedly the native UI framework for Windows but which competes with old-style Win32 (targeted by Windows Forms) and the DirectX-based WPF (Windows Presentation Foundation).

The easiest way to get started with Reactor is via the winapp CLI. Install the latest version and type winapp new selecting Reactor MVU App.

Creating a Reactor app with winapp.

The template coincidentally creates a counter app similar to the one in Chohfi’s post. The UI is coded in a Render method and there is no XAML file, everything is done in C#.

The Reactor demo app in Visual Studio Code.

Chohfi’s variant, which is also in the docs, is simplified but functionally the same. The template demo app calls UseReducer, whereas the documented demo calls UseState.

This may seem a terrible time to introduce a new (first previewed at Build in May) C# framework for desktop Windows. The niche for Windows desktop apps, mainly business applications, continues to shrink. Developers already face too many choices. Legacy .NET applications generally use Windows Forms or WPF, both of which still work.

It is hard to see many React developers wanting to switch to WinUI, when there are many ways to code desktop applications in JavaScript or TypeScript, including React Native, which seems a more natural choice.

Another issue is that this is not cross-platform. Coding a new application for Windows only seems short-sighted in most scenarios, hopeless for the consumer market, and for business use limited to companies standardised on Windows. That said, there is always an argument for using native frameworks on each platform, if the resources exist to build WinUI for Windows, SwiftUI for Mac and so on.

There is a Rust variant of Reactor and one can see this being of considerable interest, to Microsoft internally as well as for other developers. AI plus Rust is a potent combination.

There are indications that Microsoft is serious about Reactor, particularly in the remarks in Chohfi’s post about new Reactor controls being “candidates to land in WinUI itself,” and that “we’re actively working with the C# team” such that Reactor may influence the C# language.

I was also interested in Chohfi’s remarks about the mental model required to understand application code. For a XAML-based app, he said that “what does this screen look like when Count is 5 is a question you answer by reading three files and mentally running a binding engine. In Reactor, that last question has a very boring answer: read Render().”

I suspect that this is a reason for the continuing appeal of the Windows Forms framework. The mental model seems easy: one places controls on a canvas, sets their properties, and for interactivity one can just double-click a button and write the code that will run. This does not work so well for a complex application, but for something simple it is fine.

The MVVM (model-view-viewmodel) architecture which is common (though not required) for .NET applications has advantages, but even Microsoft architect John Gossman who was an early advocate for the pattern said that “for simple UI MVVM can be overkill” and that large numbers of bindings impact performance.

Reactor is MVU (model-view-update), as is React. In this pattern, the model is the state of the application, the view displays the state to the user, and update sends messages to update the state, triggered by user interaction or server activity.

A new era of AI-driven application rebuilds – now it is Microsoft Office and Adobe Photoshop

AI coding makes it easier and quicker to re-create existing applications with new code, side-stepping copyright concerns since copyright protects code rather than specification.

In February this year Cloudflare rebuilt Next.js with AI in one week and then followed with a WordPress-compatible CMS (content management system) called EmDash.

Brandon Thomas, a developer from Atlanta, Georgia in the USA, founded Artcraft with the goal of creating clean-room implementations of popular (and expensive) applications including Adobe Photoshop, LightRoom and InDesign; Figma; Microsoft Word, Excel and PowerPoint; AutoDesk’s AutoCAD, and more.

The applications are coded in Rust, run cross-platform on Windows, macOS, Linux and FreeBSD, and Web via WebAssembly, and are open source on GitHub under the Apache 2.0 license. The GUI is driven by the egui library, which means controls are not native but drawn by the library.

On LinkedIn, Thomas said that “we do not decompile binaries or copy Adobe Code” and “yes, I am actually an engineer.”

The ArtCraft implementations have some advantages over the commercial originals, in that they run on Linux, promise no tracking or ads or telemetry gathering, and can perform well thanks to the Rust’s efficiency.

On Hacker News Thomas said that “software is over” and that this initiative heralds a new era of escape from what he called “cellphone incrementalism and platform lock-in.”

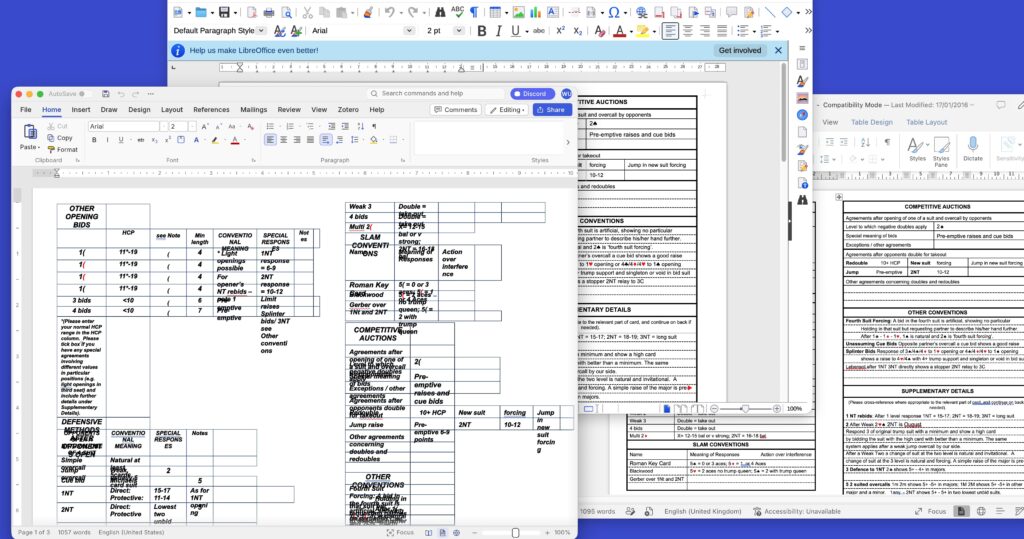
Let us not get carried away yet. I tried WordCraft (whose name I recall from a word processor for the Commodore Pet which could only hold a few paragraphs in memory before painful paging to disk) and was both impressed and disappointed. It looks great but failed to render a complex Word document which I have used before to test LibreOffice.

WordCraft scrambled this awkward Word document

It is early days though and no doubt these and other issues will be fixed; most of the ArtCraft applications are described as Alpha releases.

Although the clean-room method is well established as a defence against copyright infringement, it does not remove patent restrictions. It is also now obvious that treating code as the essence of an application’s intellectual property is no longer possible and one must expect legal arguments if these applications, or other similar works, gain ground.

Nevertheless, the assumption that recreating applications to escape vendor lock-in is too expensive and difficult is now breaking down.; it is a big change for the industry even if, right now, it is hard to see all the implications.

Deno’s endo – team joins CloudFlare, runtime will be abandoned in one year’s time

Deno (and Node.js) inventor Ryan Dahl has posted that his team is joining Cloudflare and that after one more year of support “we will end our development of the Deno runtime. Deno will remain open source, and we welcome others who want to continue its development.”

Deno 1.0 was released in 2020 as an attempt to fix what Dahl called “design mistakes in Node”. Deno is built in Rust, supports TypeScript natively, takes advantage of V8 sandboxing, but at launch did not support Node modules, limiting compatibility.

Deno’s initial take-up was limited by lack of Node.js compatibility, a problem the project attempted to fix in Deno 2.0, released in October 2024. Retro-fitting Node.js compatibility must have been a big drain on resources, absorbing effort that could have gone into improving the runtime.

In the meantime, Node.js worked on adding native TypeScript support, delivered in early 2025 by Node.js 23.6 in experimental form.

Deno also suffered from the rise of Bun, another JavaScript runtime and bundler, first released in September 2023, with TypeScript support, some Node.js compatibility, and fast performance. Bun evolved rapidly and was acquired by Anthropic in December 2025. Bun continues to improve, with the latest 1.4.3 release adding a TypeScript type checker which is a port of Microsoft’s typescript-go (now just TypeScript 7) to Rust, with a claimed 3x performance improvement.

The Deno project’s business model depended on enterprise support contracts and hosting via Deno Deploy, perhaps not sufficient for the long-term health of the project.

Dahl writes that “we know this is a consequential change for people who have built on Deno,” but offers little comfort to users. Deno Deploy will be discontinued in 6 months. The JSR registry, designed as a superset of the npm registry and as TypeScript-first, will continue.

On Reddit Deno users debate where to go. Might Deno survive as an independent open source project (unlikely)? One says: “we are all back to Node these days” and another, “perhaps now is a good opportunity to consider .NET.”

GitHub reliability and scalability: a consequence of AI and too much for free

GitHub’s CTO Vlad Fedorov has posted apologetically about the 17th August outage which, he said, “lasted 7 hours and 47 minutes. It disrupted github.com, authentication, GitHub Actions, APIs, pull requests, issues, and Copilot, affecting developers and organizations around the world.”

As if that is not bad enough, Fedorov also apologised for a failure of Actions on August 6th; and GitHub users will be aware of other incidents over the last few months that have tarnished the company’s reputation as well as being costly for its customers.

GitHub is owned by Microsoft and there is a narrative that says: under Microsoft GitHub has lost its best engineers and is now suffering from that as well as issues with the Azure platform.

There may be something in that, but there are more obvious reasons for GitHub’s difficulties. Specifically, Fedorov states that “since April, monthly commits have grown from 1.4 billion to 2.9 billion.”

That is a rapid growth in demand for a platform that was already under stress. Agentic AI appears to be a large part of the reason. Pull requests and requests are no longer generated mainly by humans, but are now programmatic and therefore created more quickly. In addition, AI-driven development means that it is no longer necessary to be a developer in order to create software projects; more people are creating more software with AI assistance.

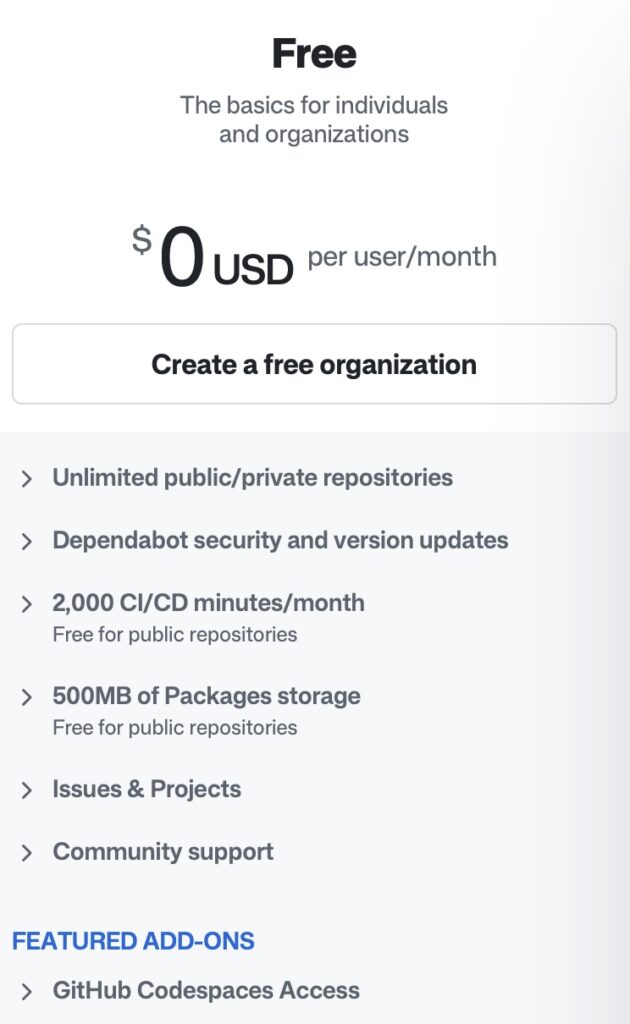
GitHub has long had an amazing free offer. Take a look: free plans include unlimited public or private repositories as well as 2,000 CI/CD minutes every month, or unlimited for public repositories. For just $4.00 per month those limits increase. Competitors such as GitLab have reduced their free offer but GitHub has not.

GitHub’s generous free plan

GitHub is Microsoft and can afford it, right? True but free (or too cheap) has a hidden cost, if scaling problems impact paying customers, as has happened.

A way of managing this is to run isolated platforms within GitHub such that an issue affecting some users does not automatically impact all users. It appears that GitHub’s architecture prevents this at the moment.

Part of the answer, as Fedorov discusses, is to improve and expand GitHub’s scalability. A post in April describes this work and includes the comment that “we started working on path to multi cloud,” meaning that Microsoft is willing to pay competitor cloud companies in order to fix these issues.

It seems to me though that Microsoft/GitHub also need to restrain agentic AI by means of quotas and higher prices, in the interests of maintaining the stability of the platform. If that also means reducing the free offer that is understandable; better to have a reliable platform than a free one. Docker, for example, went through this kind of transition, though in that case it was a matter of financial necessity.

In the meantime Cursor (now part of SpaceX) has introduced Origin, now in public beta as a “git forge for storing and sharing code”, which Vicent Martí described in technical detail as Git at any scale. Marti was formerly at Planetscale and before that, GitHub.

The technology is fascinating, but I suspect Cursor also has in mind not to replicate GitHub’s mistake in underpricing its platform.

Linux on the desktop: growing, but not by as much as some claim

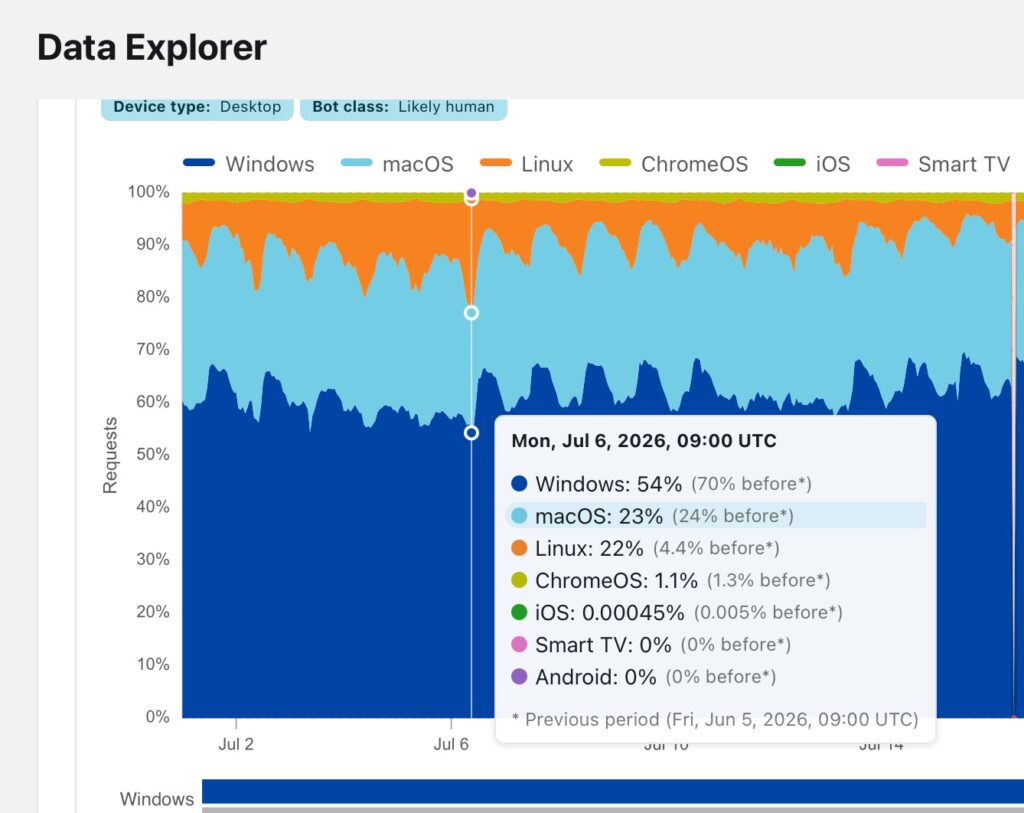
My attention was caught by the claim that Linux desktop use “surged to 22% on one workday.”

Unfortunately the claim does not stand up to scrutiny. The figures are drawn from Cloudflare data and based on North America only. The 22% is there but only at 9:00 UTC, which is 4:00am on the east coast and 1:00am on the west coast, or in other words, when most of the USA is asleep. At 15:00 UTC on the same day, Linux share was down to 6%.

Figures showing Linux share of 22% in North America - but only when most people are asleep
Figures showing Linux share of 22% in North America – but only when most people are asleep

If you set Cloudflare to show global figures, they are more even, with Linux desktop usage tending to peak at around 7%. Windows remains dominant.

I agree though with reporter Steven Vaughan-Nichols that Microsoft has damaged Windows with intrusive advertising and other user-hostile moves, such as the wrecking of the Start menu, the central position for the taskbar, and the confusing repositioning of key options like Copy on the right-click menu in File Explorer.

Almost whenever I touch a Windows 11 machine on behalf of another person, I offer to move the taskbar back to left alignment, and so far every single person has preferred it that way. There’s a good reason: the left corner is easier to hit with the mouse pointer. The central position was a victory for cosmetics over usablity.

I digress though. Today it looks unlikely that Windows on the desktop will be displaced by Linux; however what is more important is the desktop computing continues to be displaced by mobile and web. The notion of a home PC died long ago, other than for gaming.

My bank is “improving” its web site for online banking, in fact making it worse for desktop users. It justifies this by saying it will be better on mobiles. It is annoying but may be the right thing from the bank’s perspective.

In my own area, software development, desktop PCs remain more suitable than any other form factor, though I confess to using a Mac most of the time now (Windows 11 was my break point). On Windows, WSL (Windows subsystem for Linux) has become near-essential.

I also still use Word, Excel and Outlook so Microsoft continues to get money from me.

Getting started with Azure Artifact Signing

Signing applications is a requirement for deploying a desktop or mobile application and can be fiddly. Microsoft’s Azure Artifact Signing always looked to me like a good solution in that the pricing is reasonable at $9.99 per month for up to 5,000 signings, and it is run by Microsoft so one would think that the certificates will be satisfactory for Windows users.

This week I got started with the service. Microsoft has a handy quickstart guide and the first thing to note is that availability is limited to USA and Canada for individual developers, or USA, Canada, EU and UK for organizations. Luckily I work for a small UK limited company so qualify as an organization.

I also noted that a pay as you go Azure subscription is required; if you have a sponsored subscription that will not work.

The first step is to create an Artifact Signing Account. Billing starts from when this account is created, even if you are unsuccessful in obtaining a signing certificate. Should this be the case, make sure to delete the account.

Next, check the roles assigned to the user that will operate the code signing. There are two: Artifact Signing Identity Verifier and Artifact Signing Certificate Profile Signer. I assigned them both to my Entra ID user.

Now there are two steps to obtaining a certificate profile. The first is Identity Validation. In my case this is for an organization; you will need a DUNS number, two valid email addresses, a functioning web site, and the first and last name of the individual that will use the service. The organization address should match the one recorded at Companies House, even if day to day work is done elsewhere.

The organization identity verification automatically progresses to individual identity verification. In my case this was done by a company called AU10TIX and I was able to use a UK driving licence.

Next I hit what looked like a roadblock. I received an email asking me to verify my email address; however clicking the link got me a web page stating “the request is blocked” and “service unavailable”. Thinking that perhaps the service was unavailable, I tried several times and on different networks. I am not the first to experience this. I was on the point of raising a support case when I got a further email advising that validation was complete.

Once identity validation is complete you can create a certificate profile. The type I need is called Public Trust. I had several mysterious failures with uninformative errors; I suspect this might be to do with non-unique profile names but no idea really. Again I was on the point of contacting support when I tried a new profile name and it worked.

The quickstart guide ends at this point and the next document you need is the one on setting up signing integrations. You will need a recent Windows SDK including SignTool.exe, the .NET 8.0 runtime, and the Azure Artifact Signing client tools, if like me you want to sign a Windows executable.

Then you need to create a JSON file traditionally called metadata.json, and a command to sign the file. The command will be lengthy so fire up Notepad or similar and put it in a .cmd file or similar. You need to discover the location of SignTool and the location of Azure.CodeSigning.Dlib.dll and note that there are different x64 and x86 versions.

The command includes a timestamp without which the code signing is useless as the certificate has a lifetime of just three days.

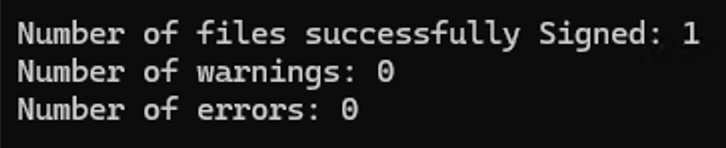
I carefully assembled the command and I am happy to report that it worked first time.

Output from code signing command

So far so good. The whole process is somewhat intricate but I am hoping this will prove a good solution for Windows.

No Mono in Microsoft’s cross-platform MAUI framework on .NET 11 – and a quick hands-on

Microsoft has released preview 6 of .NET 11, for which release is expected in November, including a big change to MAUI (Multi-platform App UI): it now runs only on .NET Core, rather than the Mono runtime.

Principal product manager David Ortinau reports that “your app builds and runs on CoreCLR, the same runtime behind ASP.NET Core, your cloud services, and desktop .NET.”

According to Ortinau, performance is generally faster than Mono on iOS and Mac Catalyst. The implication is that it is slower on Android, though he does say that it is within 10% on startup and app size. Selecting Mono is no longer an option, and the only use of Mono in .NET 11 is for Blazor WebAssembly.

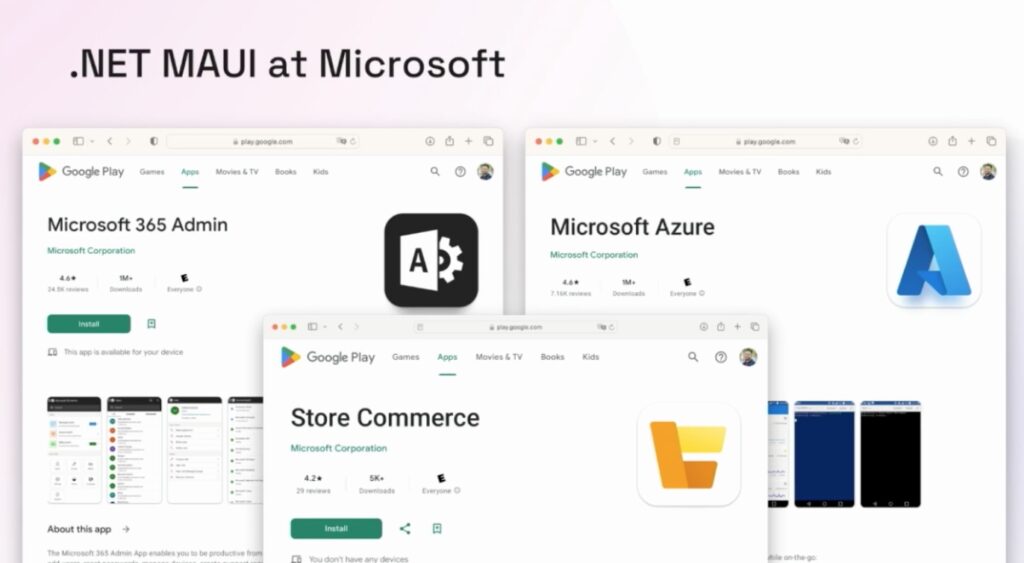
There is a key remark in Ortinau’s post. “We have worked closely with first party .NET MAUI apps validating our progress, and have received feedback from several others,” he says. The question developers may ask: what first party .NET MAUI apps? Microsoft does not use MAUI for its well-known cross-platform apps such as Teams or Office. In 2023, the company said it uses MAUI for its 365 admin, Azure admin and Store Commerce apps, though I do not know if this is still the case.

Slide from .NET Conf 2023 showing some limited use of MAUI at Microsoft

Developers would have more confidence in MAUI, both for its quality and its long-term future, if Microsoft itself made more use of it.

That said, the company does seem to be putting substantial effort into MAUI for .NET 11. Along with the CoreCLR work there are other updates in this preview. Microsoft states that the focus in .NET 11 is “to improve product quality” and this is something developers will be happy about; in some cases a statement like this might imply neglect but for MAUI it is exactly what is needed.

I have a demo MAUI project and decided to upgrade it to the new preview, working with Visual Studio Code on a Mac. It was not as easy as I had hoped. The process involved not only updating the target framework, but also the minimum versions of Android, iOS and Mac Catalyst. Then the Android SDK had to be updated, with an annoyance related to the recommended:

dotnet build -t:InstallAndroidDependencies -f net11.0-android “-p:AndroidSdkDirectory=[your path to the Android SDKs]”

The command failed with an error about the Android SDK licenses not being accepted. The fix is to set an environment variable:

export AcceptAndroidSDKLicenses=True

and then it works, though I’m not sure how this satisfies the lawyers. I also had an error where

builder.Logging.AddDebug();

could not find the AddDebug method; the fix was to add a package reference to Microsoft.Extensions.Logging.Debug to the .csproj file.

With all that done, the “Start debugging” command is not working for me in VS Code. I get a message that the “configured debug type ‘coreclr_mobile’ is not supported, and an instruction to install coreclr_mobile Extension; clicking this button gets me “no extensions found.” Update – this was resolved after updating both the C# and C# Dev Kit extensions to pre-release versions (.NET MAUI was already pre-release).

However, dotnet run from the command line works:

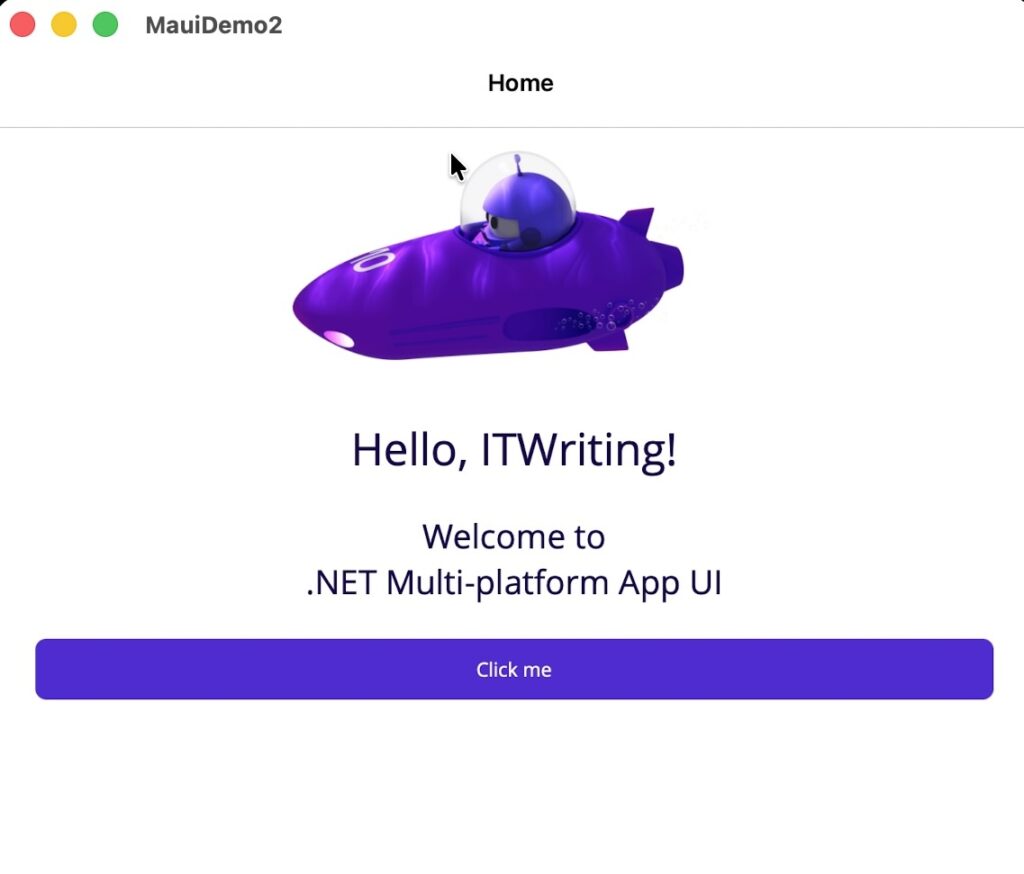
Demo of MAUI using .NET 11 Preview 6 on a Mac

I plan to do some more experimentation; note that this is a preview of .NET so some friction is expected.

Avalonia UI vs Microsoft’s .NET MAUI

What framework to choose for a cross-platform .NET GUI application continues to be awkward, with multiple good-ish options but no obvious first choice.

The three leading contenders are Microsoft’s MAUI (multi-platform app UI), third-party Avalonia UI, and third-party Uno Platform.

Joseph Tomkinson, head of software engineering at the British Heart Foundation, has an excellent post on the pros and cons of MAUI vs Avalonia UI, noting the fundamental difference that MAUI wraps native controls while Avalonia UI does all its own rendering. Tomkinson argues that MAUI has stronger mobile support (since this has only come recently to Avalonia) but that Avalonia has advantages in consistency, desktop performance, and Linux support.

A concern with Avalonia UI has been the drift towards important features becoming commercial-only, not unreasonable but a barrier to adoption for some developers. That has improved though since a sponsor appeared to fund Avalonia open-source development. CEO Mike James (formerly at Xamarin and then Microsoft) has posted about the difference this has made.

According to James, the Avalonia UI team has more than doubled, to 20 people, and now includes a QA lead. He says usage is growing:

“In the whole of 2025, Avalonia projects were built over 122 million times. In the first six months of 2026 alone, that figure has already passed 410 million.”

I am not sure exactly what this metric is counting – telemetry every time a developer builds a project? – but presuming it is like with like, that is impressive.

On the MAUI side though, one thing Tomkinson notes is that third-party components are more widely available, because it is an official Microsoft framework, and that quality is much better now than it was early on.

The BigCorp factor is not entirely in MAUI’s favour though. Microsoft might change direction and decide MAUI is no longer important, particularly as its own internal usage of the framework still seems minimal.

I am inclined to try building an example project in both frameworks to get my own feel for which would work best.

A mild case of Azure bill shock: is this the most over-priced service on Microsoft’s cloud?

I have been experimenting with accessing Azure storage from remote PCs and tried out the option to use SFTP which was introduced last year. It works though there are limitations, like no support for SSH commands after connecting, no resume support for uploads, and no support for Azure AD authentication – this last is a bit of an issue since fine-grained permissions can only be done with local users, specific to the blob storage.

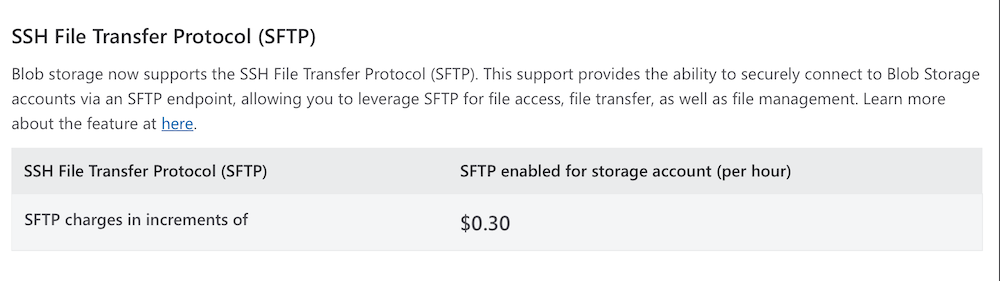
I actually thought I had turned this off after my experiment but I did not. So I had SFTP enabled on a test storage account, doing nothing. I spotted it of course when I got a large (for my usage) bill. Simply having SFTP enabled on a storage account costs around $220 per month.

To be fair to Microsoft, the cost is documented and there is a notice in the portal, in the details for the storage account, that enabling SFTP incurs a charge, though it does not say how much.

The cost for enabling SFTP

The price is remarkable though, especially given that it seems that the SFTP support is a bit of a hack. Perhaps Microsoft actually runs up a dedicated VM for this in the background, who knows?

“The cost is astronomical considering the service, it’s like $7.20 a day to use and roughly $220 a Month. It’s WAY cheaper to use a VM. This service is like 3x too much,” said a comment from another sufferer.

My advice is not to do this. My further advice is to track closely the actual spend on any new services you run up since is it the only reliable way to avoid this kind of problem.