Category Archives: microsoft

Microsoft Build and the repositioning of Windows

Microsoft Build is under way in Seattle, with around 6000 attendees here to learn about the company’s latest developer technology. But what is the heart of Microsoft’s platform today? The answer used to be Windows – and this conference was originally the Build Windows event, distinct from the earlier Professional Developer Conference which was run by the Developer Division and had a wider scope.

image
Microsoft’s Satya Nadella introduces Build 2019 

  Today though it is not so clear. The draft Build 2019 press release hardly mentions Windows. Here is the summary of topics: 

In his opening keynote, Microsoft CEO Satya Nadella outlined the company vision and developer opportunity across Microsoft Azure, Microsoft Dynamics 365 and Power Platform, Microsoft 365, and Microsoft Gaming”

Windows is there of course. Azure uses Hyper-V, the Windows Server hypervisor. A Microsoft 365 license is a bundle of Office 365, InTune device management, and Windows Enterprise. Microsoft Gaming includes PC gaming, and Xbox gets its name from the Windows DirectX hardware accelerated graphics API. But no, this is no longer a conference about developing for Windows, and Microsoft seems happy for its operating system to be less visible. PCs remain the devices on which many of us get most of our work done, but it is not a growth market, and cannot really become one unless by some miracle Microsoft returned to mobile or wearables. That would be hard, especially since the Universal Windows Platform, originally conceived as an app platform for touch and mobile as well as desktop, has drifted away from that concept and become something of uncertain relevance unless you are targeting HoloLens or some other niche.

That said, Windows is still evolving and Build remains the best event to keep track of what is new. In the advance news on which this post is based, several key features were announced.

Windows Subsystem for Linux 2 (WSL) now supports Linux Docker containers as well as faster file I/O. This also integrates nicely with new Visual Studio Code Remote Development Extensions which let you edit and debug code in WSL, in Docker containers, or on any remove machine over SSH.

Windows Terminal is a new application for command lines including PowerShell, Cmd and WSL. It includes rich fonts (with hardware accelerated rendering), multiple tabs, and “theming and customization”.

React Native for Windows is an open source project on GitHub that will let you develop high performance Windows applications.

MSIX Core is the next step in Windows setup technology and lets you install MSIX packages on Windows 7 as well as Windows 10.

.NET 5 has been announced and seems to embrace both Windows Desktop and cross-platform – I will be unpacking the details of how this works shortly. .NET 5 will release in 2020.

Microsoft Edge (on Chromium) has new features announced included an IE mode tab (for running Internet Explorer applications/sites), three levels of privacy (Unrestricted, Balanced and Strict) which claim to control third-party tracking, and Collections which is a feature for collecting and sharing web information and integrates with Office.

Of course there is much more news on what Microsoft now sees as its top priority topics: Azure, AI, Microsoft Search, PowerApps, PowerBI, Cognitive Services, Bot Framework, Mixed reality, IoT and Edge computing, Cosmos DB, Azure Kubernetes Service, GitHub and more.

Windows? Still the best way to run Office, and excellent for developing applications. But this is Microsoft Build, not Build Windows.

image
Seattle, Washington the evening before Microsoft Build

Microsoft Office and privacy: happy to send what you type to the cloud for analysis?

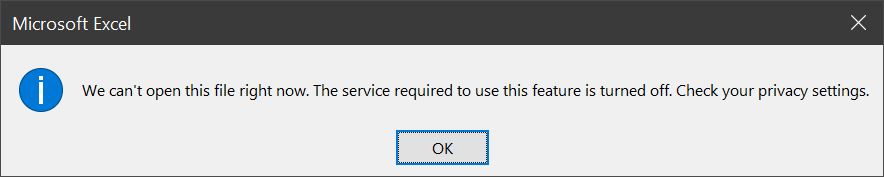
I attempted to open a document from on-premises SharePoint recently and was greeted with an error asking me to check my privacy settings.

image

“The service required to use this feature is turned off” I was informed. Hmm, what service is that then? The solution turned out to be in the new Office privacy settings, just as the dialog suggested.

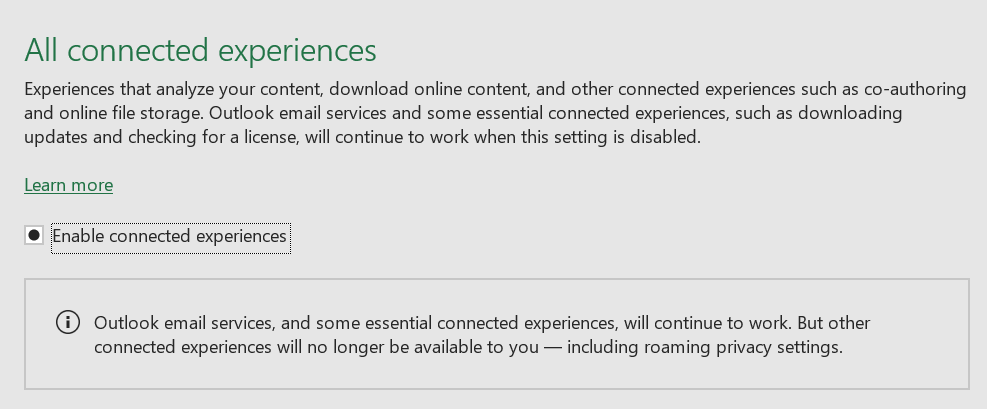
If you disable what Microsoft calls “Connected experiences” it appears to block access to SharePoint. Probably not what the user intended.

image 

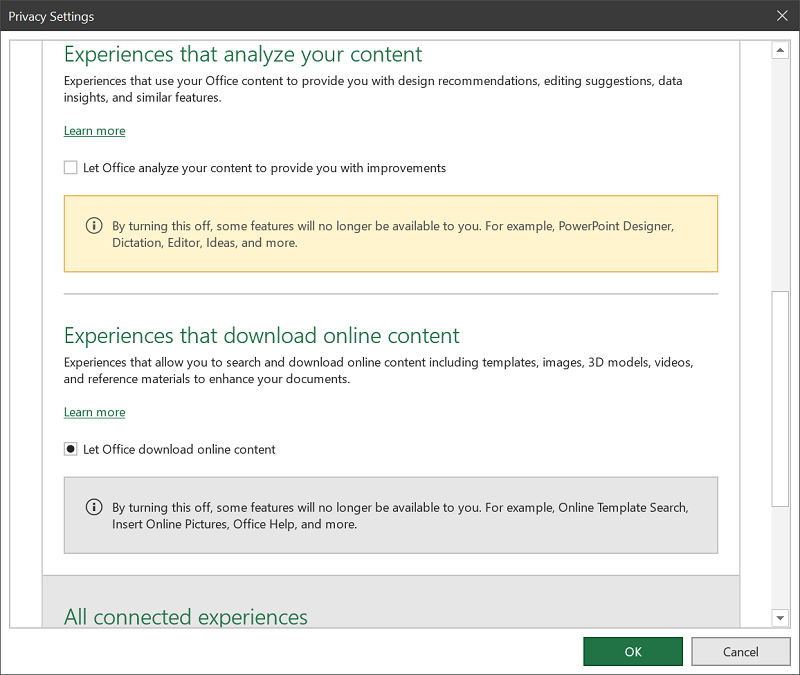
This setting is not great for clarity. Privacy-conscious users like myself may disable it because it represents your agreement to “experiences that analyze your content”. Since this means uploading your content to the cloud for analysis it sounds as if it might weaken both privacy and security. If you look at all the options though, it may be possible to agree to access online file storage without agreeing to content analysis:

image

It looks as if by unchecking “Let Office analyze your content” you might be able to stop Office uploading your stuff.

Is there anything to worry about? We need to know more about what happens to our data. There is a Learn More link that takes us here. This lists lots of features but does not tell us what we want to know. Maybe here? This tell us that:

Three types of information make up required service data.

  • Customer content, which is content you create using Office, such as text typed in a Word document, and is used in conjunction with the connected experience.

It is still not clear though what happens to our data, other than that it is “sent to Microsoft”. Even the massive Microsoft Privacy Statement is no more illuminating on this point. In fact, it is arguably rather alarming since it contains this statement:

Microsoft uses the data we collect to provide you with rich, interactive experiences. In particular, we use data to:

  • Provide our products, which includes updating, securing, and troubleshooting, as well as providing support. It also includes sharing data, when it is required to provide the service or carry out the transactions you request.
  • Improve and develop our products.
  • Personalize our products and make recommendations.
  • Advertise and market to you, which includes sending promotional communications, targeting advertising, and presenting you with relevant offers.

We also use the data to operate our business, which includes analyzing our performance, meeting our legal obligations, developing our workforce, and doing research.

In carrying out these purposes, we combine data we collect from different contexts (for example, from your use of two Microsoft products) or obtain from third parties to give you a more seamless, consistent, and personalized experience, to make informed business decisions, and for other legitimate purposes.

This suggests that Microsoft will profile me and send me advertising based on the data it collects. What I need to know is not only the fact that this happens, but also the mechanism, in order to make an informed judgement about whether it is sensible to enable these options. Of course it is also possible that the Office content analysis service does not do this. I am guessing.

What can go wrong? These risks are hard to quantify. If you are typing something confidential, it makes sense not to share it more than is necessary, as further sharing can only increase the risk. There are some interesting scenarios too, such as what happens if Microsoft receives a legal demand to have sight of the content of your documents. Microsoft may not want to give access to your content, but in some circumstances it might not have the choice. Then again, I doubt it retains content sent for the purpose of personalisation, beyond whatever factors the service determines are significant. However this is not stated here.

Is this any different from storing documents on a cloud service such as SharePoint / OneDrive online? It is a bit different since in the Office case you are permitting Microsoft to analyze as well as to store your content.

All of this is up for debate. I accept that the risks are probably small as well as the fact that the wider world has little or no interest in most of the content I type but do not choose to publish.

Nevertheless, there are a few things which seem to me reasonable requests.

– A clear statement concerning what happens to my content if I choose to let it be analyzed by Microsoft’s cloud service, to enable better informed decisions about whether or not to enable this feature. Dumping the user into an all-encompassing privacy policy is not good enough.

– Improved settings (and possibly some fixed bugs) so that privacy-conscious users do not inadvertently disable access to on-premises SharePoint, as in my example, or other unexpected outcomes.

– A simple way to exclude a specific document from the service, conceptually similar to “in-private” mode in a web browser though with more chance of actually protecting your privacy (in-private mode is not really very private).

In general, I do not think the solution to a customer’s reasonable concerns about privacy and security of personal information is to obscure how this data is handled.

A post that can save you money: scheduling Azure Virtual Machines for start/stop

I have written recently about Windows Virtual Desktop, the ability to set up a virtual desktop environment on Azure at a relatively low cost, provided your users have Microsoft 365 accounts. My test setup is minimal but I have been watching the cost which is currently working out at £5.39 per day. This excludes the cost of Microsoft 365; it is purely for the infrastructure including VPN gateway, storage and VM. Bandwidth is a variable cost but almost negligible on my usage. Of that cost, the VM is around 75%. So if I could shut down the VM when not in use the savings are substantial.

It turns out this is pretty easy on Azure though it requires some plumbing. VMs do have a built-in option to shutdown on a schedule, but not to start up. To get start/stop, you need an Automation Account.

image

With the automation account created, select it, hit Start/Stop VM, then click “Learn more about and enable the solution”.  You get this dialog.

image

Here we learn that to save money, we have to spend it, on three new services: Automation, Log Analytics, and Monitor. It is not too bad though as there is a free tier for these services that may be all I need. Hit Create.

image

In this window you have to configure three sections. Nothing challenging, but note that in Configuration you set the Target Resource Group Names. No pick list here, you have to type in the names. Or use a wildcard, which is unlikely to be a good idea since by default it will start and stop ALL your VMs. The schedule is not very smart, just a daily on and off, but see below. Once done, click Create to add the solution.

All done, but what about weekends, for example. This is easily fixed if you create your own schedules. Just go into your automation account and click Schedules under Shared Resources. The wizard-created schedules are listed, and you can modify them or create new ones. It looks as if you might need 5 schedules, one per weekday, recur every week, to make your VMs not run at weekends. There is no Monday-Friday option.

More documentation here. Note that automation can also run PowerShell scripts which will be even more flexible.

Scheduling cloud resources to shut down when not in use must be one of the most effective ways to reduce IT spend.

Update: here is the outcome of my efforts:

image

The Management resource group has the runbook that performs the start/stop action. The cost of this is small. Overall cost has gone down by about £2.00 or about 40% in my case. I appreciate this is a very small test deployment, but it would support maybe 4 or 5 users without any problem and my experience shows that you can indeed make a large saving by scheduling VMs to stop when not in use.

Microsoft Financials: strategic purpose of Github, Teams and PowerApps revealed

Microsoft has announced its quarterly financial statements, reporting revenue of $30.6 billion, up 14% on the same period last year.

The story seems to be largely more of the same, which is good for the company in that all its numbers look good.

The most striking figure is 73% increase in Azure revenue. Azure is the smallest of its three self-defined segments though, though all three are similar in size. “More Personal Computing” (Windows, Surface and gaming) delivered the most revenue, followed by Productivity and Business Processes. That said, at this rate of growth Azure will soon be the biggest of the three segments.

Aside: has there ever been a dafter segment name than More Personal Computing? More than what?

Quarter ending March 31st 2019 vs quarter ending March 31st 2018, $millions

Segment Revenue Change Operating income Change
Productivity and Business Processes 10100 +1236 3979 +864
Intelligent Cloud 9649 +1780 3208 +554
More Personal Computing 10680 +763 3154 +631

The segments break down as:

Productivity and Business Processes: Office, Office 365, Dynamics 365 and on-premises Dynamics, LinkedIn

Intelligent Cloud: Server products, Azure cloud services

More Personal Computing: Consumer including Windows, Xbox; Bing search; Surface hardware

Some points to note. Microsoft reported a “material improvement” in Azure gross margin, something which does not surprise me. In my experience, the Azure Portal does a great job (from Microsoft’s perspective) in steering you towards premium services and extras, as I found when trying Windows Virtual Desktop – check my note on the VPN Gateway at $140 per month).

Office 365 is still growing, up 30% according to Microsoft’s slides. LinkedIn is also increasing revenue, up 27%.

Despite Chromebooks and mobile, Windows is still a cash cow with revenue from Windows OEM Pro up 15% year on year. Consumer revenue is down 1%.

In the earnings call CEO Satya Nadella called out Teams as “bringing together everything a team needs” (well, apart from a proper shared calendar).

CFO Amy Hood remarked on what she called “strategic areas” by which she means I think areas that drive adoption:

We will invest aggressively in strategic areas like Cloud through AI and Github, Business Applications through Power Platform and LinkedIn, Microsoft 365 through Teams, Security, and Surface as well as Gaming.

Note that Github is seen as a way of persuading developers to use Azure services, and note also the important attached to the Power Platform. Power platform? Here it is:

The Power Platform is today comprised of three services – Power BI, PowerApps and Flow … It is a system that enables users to do three key actions on data that help them drive business: Analyze, Act, and Automate. We do this with Power BI, PowerApps, and Flow, all working together atop your data to help EVERYONE, from the CEO to the front-line workers, drive the business with data.

says CVP James Phillips.

The piece that particularly interests me is PowerApps. Microsoft spent years looking for a modern successor to Visual Basic, app development within reach of non-specialists (kind-of). In PowerApps it believes it has the answer:

PowerApps is a “citizen application development platform” – allowing anyone to build web and mobile applications without writing code. The natural connection between Power BI and PowerApps makes it effortless to put insights in the hands of maintenance workers, teachers, miners and others on the frontline, in tailored and often task-specific applications

says Phillips.

So if VB was a driver for Windows adoption, then PowerApps will push you towards Microsoft’s cloud-hosted business applications.

Microsoft Planner: a good task management solution for small teams?

It is a common scenario for any team: you have projects which break down into various tasks, and you need to assign tasks to team members with deadlines. The low-tech solution is that you have a meeting, you assign the tasks, and each person organises their time in whatever way works for them. A calendar entry with a reminder, perhaps, or a task entry with a reminder, if you use Outlook and Exchange or Office 365.

But what if you want a project-level view of how the tasks are going? Again there are low-tech solutions like Excel spreadsheets or even a whiteboard on the wall. Of course there are software solutions as well. On Microsoft’s platform (which is the subject of this post) you could use Microsoft Project. A user license for Project Online Professional is currently £22.60 per month, though, more than double the cost of an Office 365 Business Premium account (£9.40). Even a team member license (Project Online Essentials) is £5.30. It seems a big leap in cost, and is more than many businesses need in terms of features.

There is an alternative, which is Microsoft Planner. This is one of those Office 365 apps that is not all that well known, and it comes for free with most Office 365 plans. It gives you basic project management, with the ability to assign tasks to team members.

You can find Planner by logging into Office 365 and choosing Planner from the All Apps view.

image

Once Planner opens you can create a plan.

image

I advise a careful look at this dialog before clicking Create plan. If you have one big project, such as perhaps a new product you are developing, a plan dedicated to that project makes sense. If you have multiple small projects though, it would be better to have a single plan to contain multiple projects. The reason is that plans have a relatively high overhead. Each plan by default creates an Office 365 group and an Office 365 Sharepoint site. This could easily become a maintenance nightmare. Within a plan though, you can have multiple buckets, and each bucket can contain multiple tasks.

Note also that you can use an existing Office 365 group. It might make sense to create the group first, if only to get a sensible name. By default, the group gets the game of the plan. Only one Sharepoint site is created per group, so this is more lightweight (phew!).

After thinking this through you hit Create plan. The plan is created and you can get on with adding tasks, the base unit of a plan.

A few things about tasks:

– they have due dates

– they are assigned to one or more team members

– they can have checklists of sub-tasks which you check off

– they can have attachments

– they have a status of “Not started”, “in progress”, or “complete”

image

Tasks can be grouped into buckets (a good idea). Once you have a few tasks you can view charts showing progress and a schedule showing when task completion is due.

image

When members are assigned a task, they get an email notification.

image

And as I mentioned there is Sharepoint site which can have all sorts of junk added to it.

image

Now a few observations. Planner looks useful but as so often with these Microsoft apps, there are things that make you want to bang your head against the nearest wall. The most obvious problem is that Planner tasks do not integrate with Outlook tasks. The best you can do is to export the plan schedule to an Outlook calendar. Guess what is the top user request for Planner?

image

From here we learn of an added complication, that Outlook tasks are being replaced by Microsoft To-Do. Inevitable perhaps but I like Outlook tasks and the fact that everything is in an Exchange mailbox, and therefore easy to manage.

Still, the good news is that it says In Development.

Other limitations? Well, Planner is very basic. You cannot even have dependent tasks. You cannot set status to show the degree to which a task is complete, which even Outlook tasks can do. No Gantt charts either. Or features like milestones, cost tracking, risk assessment, time management, templates, prioritisation, projections, or other such features.

In fact, you cannot even export to Excel, the second most requested feature (the team is working on this too).

image

You cannot help but wonder if Microsoft does not want to make Planner too good, lest it cut into lucrative Project sales.

If so, this is to my mind wrongheaded. For every Project sale lost, there would be three sales won for Office 365 if it came with an excellent project management tool built in. There is also the problem of duplicated effort. Why not get the Project team to develop Project Lite for Office 365, limited by lack of some of the more advanced features, but with a smooth upgrade path, rather than making an alternative product which is still not fully ready?

Still, Planner is free with Office 365, and worth being aware of if you can get it to do what you need.

Hands on with Windows Virtual Desktop

Microsoft’s Windows Virtual Desktop (WVD) is now in preview. This is virtual Windows desktops on Azure, and the first time Microsoft has come forward with a fully integrated first-party offering. There are also a few notable features:

– You can use a multi-session edition of Windows 10 Enterprise. Normally Windows 10 does not support concurrent sessions: if another user logs on, any existing session is terminated. This is an artificial restriction which is more to do with licensing than technology, and there are hacks to get around it but they are pointless presuming you want to be correctly licensed.

– You can use Windows 7 with free extended security updates to 2023. As standard, Windows 7 end of support is coming in January 2020. Without Windows Virtual Desktop, extended security support is a paid for option.

– Running a VDI (Virtual Desktop Infrastructure) can be expensive but pricing for Windows Virtual Desktop is reasonable. You have to pay for the Azure resources, but licensing comes at no extra cost for Microsoft 365 users. Microsoft 365 is a bundle of Office 365, Windows InTune and Windows 10 licenses and starts at £15.10 or $20 per month. Office 365 Business Premium is £9.40 or $12.50 per month. These are small business plans limited to 300 users.

Windows Virtual Desktop supports both desktops and individual Windows applications. If you are familiar with Windows Server Remote Desktop Services, you will find many of the same features here, but packaged as an Azure service. You can publish both desktops and applications, and use either a client application or a web browser to access them.

What is the point of a virtual desktop when you can just use a laptop? It is great for manageability, security, and remote working with full access to internal resources without a VPN. There could even be a cost saving, since a cheap device like a Chromebook becomes a Windows desktop anywhere you have a decent internet connection.

Puzzling out the system requirements

I was determined to try out Windows Virtual Desktop before writing about it so I went over to the product page and hit Getting Started. I used a free trial of Azure. There is a complication though which is that Windows Virtual Desktop VMs must be domain joined. This means that simply having Azure Active Directory is not enough. You have a few options:

– Azure Active Directory Domain Services (Azure ADDS) This is a paid-for azure service that provides domain-join and other services to VMs on an Azure virtual network. It costs from about £80.00 or $110.00 per month. If you use Azure ADDS you set up a separate domain from your on-premises domain, if you have one. However you can combine it with Azure AD Connect to enable sign-on with the same credentials.

There is a certain amount of confusion over whether you can use WVD with just Azure ADDS and not AD Connect. The docs say you cannot, stating that “A Windows Server Active Directory in sync with Azure Active Directory” is required. However a user reports success without this; of course there may be snags yet to be revealed.

– Azure Active Directory with AD Connect and a site to site VPN. In this scenario you create an Azure virtual network that is linked to your on-premises network via a site to site VPN. I went this route for my trial. I already had AD Connect running but not the VPN. A VPN requires a VPN Gateway which is a paid-for option. There is a Basic version which is considered legacy, so I used a VPNGw1 which costs around £100 or $140 per month.

Update: I have replaced the VPN Gateway with once using the Basic sku (around £20.00 or $26.00 per month) and it still works fine. Microsoft does not recommend this for production but for a very small deployment like mine, or for testing, it is much more cost effective.

This solution is working well for me but note that in a production environment you would want to add some further infrastructure. The WVD VMs are domain-joined to the on-premises AD which means constant network traffic across the VPN. AD integrates with DNS so you should also configure the virtual network to use on-premises DNS. The solution would be to add an Azure-hosted VM on the virtual network running a domain controller and DNS. Of course this is a further cost. Running just Azure ADDS and AD Connect is cheaper and simpler if it is supported.

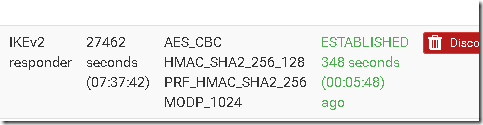
Incidentally, I use pfsense for my on-premises firewall so this is the endpoint for my site-to-site VPN. Initially it did not work. I am not sure what fixed it but it may have been the TCP MSS Clamping referred to here. I set this to 1350 as suggested. I was happy to see the connection come up in pfsense.
image 

Setup options

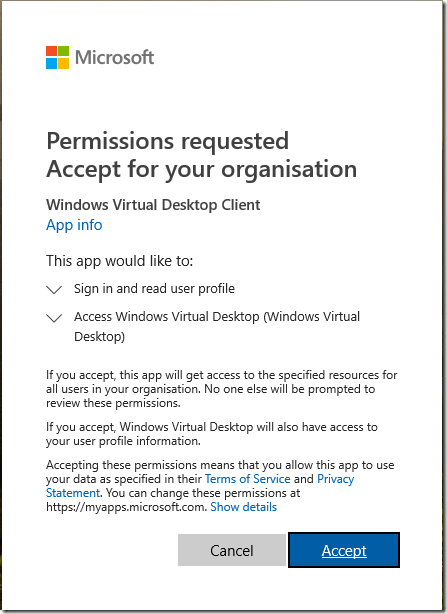
There are a few different ways to set up WVD. You start by setting some permissions and creating a WVD Tenant as described here. This requires PowerShell but it was pretty easy.
image

The next step is to create a WVD host pool and this was less straightforward. The tutorial offers the option of using the Azure Portal and finding Windows Virtual Desktop – Provision a host pool in the Azure Marketplace. Or you can use an Azure Resource Manager template, or PowerShell.

I used the Azure Marketplace, thinking this would be easier. When I ran into issues, I tried using PowerShell, but had difficulty finding the special Windows 10 Enterprise Virtual Desktop edition via this route. So I went back to the portal and the Azure marketplace.

Provisioning the host pool

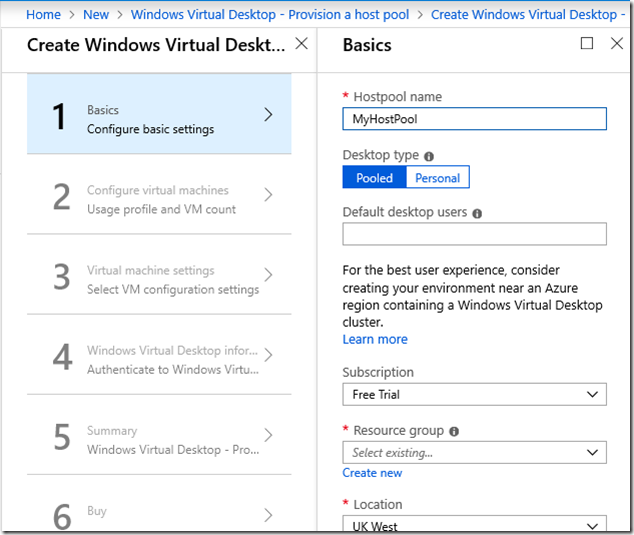
Once your tenant is created, and you have the system requirements in place, it is just a matter of running through a wizard to provision the host pool. You start by naming it and selecting a desktop type: Pooled for multi-session Windows 10, or Personal for a VM per user. I went for the Pooled option.
image

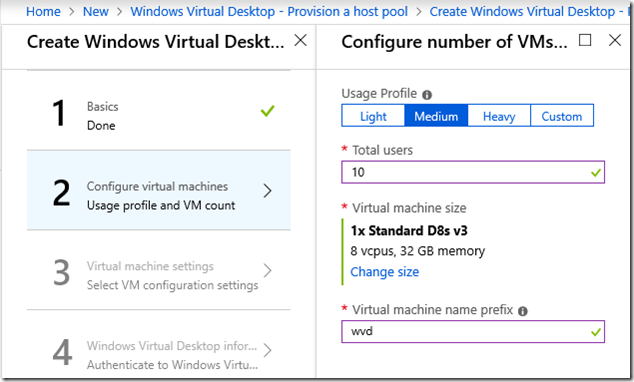
Next comes VM configuration. I stumbled a bit here. Even if you specify just 10 (or 1) users, the wizard recommends a fairly powerful VM, a D8s v3. I thought this would be OK for the trial, but it would not let me continue using the trial subscription as it is too expensive. So I ended up with a D4s v3. Actually, I also tried using a D4 v3 but that failed to deploy because it does not support premium storage. So the “s” is important.
image

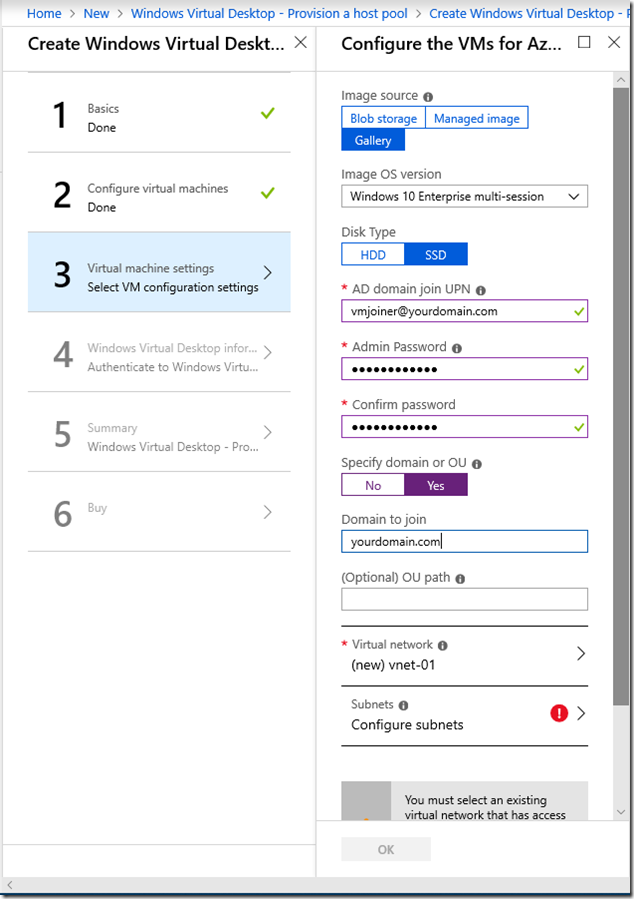
The next dialog has some potential snags.
image

This is where you choose an OS image, note the default is Windows 10 Enterprise multi-session, for a pooled WVD. You also specify a user which becomes the default for all the VMs and is also used to join the VMs to the domain. These credentials are also used to create a local admin account on the VM, in case the domain join fails and you need to connect (I did need this).

Note also that the OU path is specified in the form OU=wvd,DC=yourdomain,DC=com (for example). Not just the name of an OU. Otherwise you will get errors on domain join.

Finally take care with the virtual network selection. It is quite simple: if you are doing what I did and domain-joining to an on-premises domain, the virtual network and subnet needs to have connectivity to your on-premises DCs and DNS.

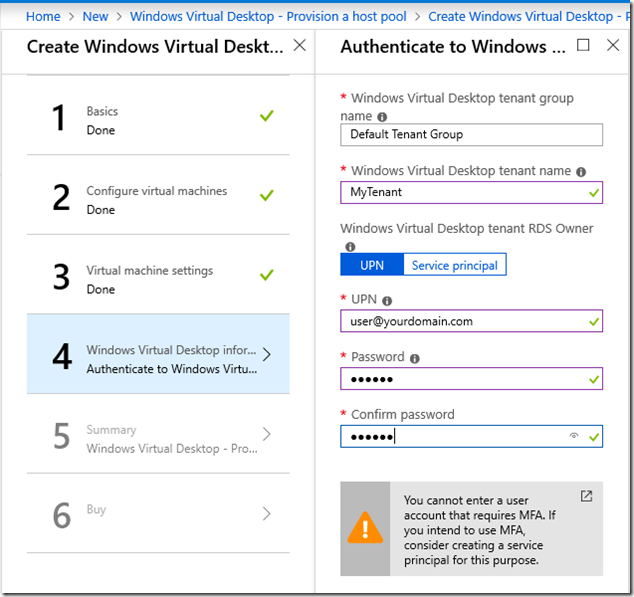
The next dialog is pretty easy. Just make sure that you type in the tenant name that you created earlier.
image

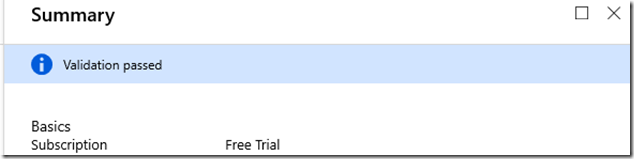
Next you get a summary screen which validates your selections.
image

I suggest you do not take this validation too seriously. I found it happily validated a non-working configuration.

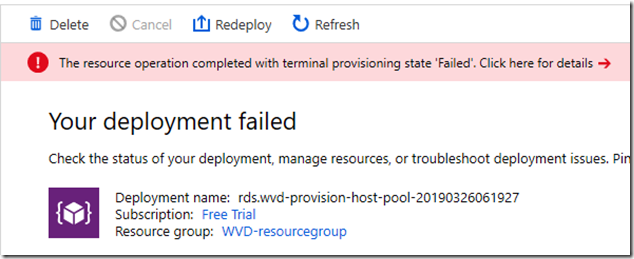
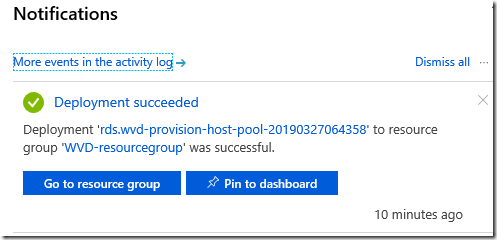
Hit OK and you can deploy your WVD host pool. This takes a few minutes, in my case around 10-15 minutes when it works. If it does not work, it can fail quickly or slowly depending on where in the process it fails.

My problem, after fixing issues like using the wrong type of OS image, was failure to join the VM to the domain. I could not see why this did not work. The displayed error may or may not be useful.
image

If the deployment got as far as creating the VM (or VMS), I found it helpful to connect to a VM to look at its event viewer. I could connect from my on-premises network thanks to the site to site VPN.

I discovered several issues before I got it working. One was simple: I mistyped the name of the vmjoiner user when I created it so naturally it could not authenticate. I was glad when it finally worked.
image

Connection

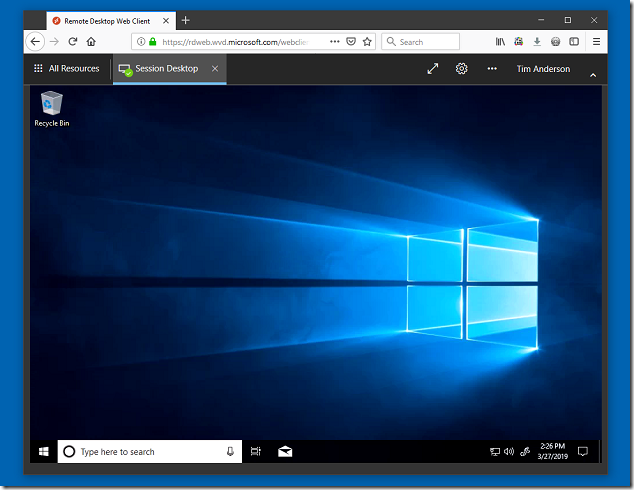
Once I got the host pool up and running my trial WVD deployment was fine. I can connect via a special Remote Desktop Client or a browser. The WVD session is fast and responsive and the VPN to my office rather handy.
image

Observations

I think WVD is a good strategic move from Microsoft and will probably be popular. I have to note though that setup is not as straightforward as I had hoped. It would benefit Microsoft to make the trial easier to get up and running and to improve the validation of the host pool deployment.

It also seems to me that for small businesses an option to deploy with only Azure ADDS and no dependency on an on-premises AD is essential.

As ever, careful network planning is a requirement and improved guidance for this would also be appreciated.

Update:         

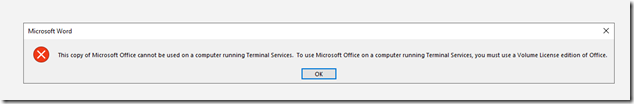
There seems to a problem with Office licensing. I have an E3 license. It installs but comes up with a licensing error. I presume this is a bug in the preview.    
image

This was my mistake as it turned out. You have to take some extra steps to install Office Pro Plus on a terminal server, as explained here. In my case, I just added the registry key SharedComputerLicensing with a setting of 1 under HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Office\ClickToRun\Configuration. Now it runs fine. Thanks to https://twitter.com/getwired for the tip.

How Windows 10 Ransomware Protection interferes with application installs

Three times recently I have had install failures on Windows 10, and three times have fixed them by disabling one of its security features.

image

“Ransomware protection” does not know anything about ransomware as such, but simply blocks access to files and folders where you are likely to store documents and data. Ransomware works by encrypting your documents and demanding money (usually in the form of bitcoin) to unlock them. Therefore blocking access prevents it from working, or at least that is the idea.

I am all in favour of blocking ransomware, but unfortunately this feature may also break application installs. Worse, they tend to break in ways that do not make the problem obvious to the user.

I installed Docker for Windows, for example (actually just accepted a prompt to upgrade) and it hung on the Installing… dialog.

Another application complained about insufficient disk space.

The problem seems to be related to application shortcuts, which are created in protected folders such as the desktop. Even though the install is running with admin rights, it cannot write these files. What happens next depends on how well the installer handles unexpected outcomes. This is not really a fatal error, but may become so.

What is the solution?

The obvious answer is to turn off controlled folder access before running installers for desktop applications. You can turn it back on afterwards.

Microsoft may say that if we all use Store apps or the Desktop Bridge packager the problem will not occur. The issue is related to the Windows legacy of free-for-all installations and the way Microsoft has been trying for many years (with partial success) to bring it under control. Mobile operating systems tend to be better behaved because they were designed to be locked down and to isolate applications from one another and from the operating system.

Office 365 vs Office 2019 vs LibreOffice: some thoughts

What has rescued Microsoft in the cloud era? It seems to me that Office 365, rather than Azure, is its most strategic product. Users do not like too much change; and back when Office 365 was introduced in 2011 it offered an easy way for businesses small and large to retire their Exchange servers while retaining Outlook with all its functionality (Outlook works with other mail servers but with limited features). You also got SharePoint online, cloud storage, and in-browser versions of Word, Excel and PowerPoint.

There was always another aspect to Office 365 though, which is that it allowed you to buy the Office desktop applications as a subscription. Unless you are the kind of person (or business) that happily runs old software, the subscription is better value than a permanent license, especially for small businesses. Currently Office 365 Business Premium gets you Outlook, Word, Excel, PowerPoint, OneNote and Access, as well as hosted Exchange and SharePoint etc, for £9.40 per month. Office Home and Business (which does not include Access) is £250, or about the same as two years subscription, and can only be installed on one PC or Mac, versus 5 PCs or Macs, 5 tablets and 5 mobile devices for the subscription product.

The subscription product is called Office 365, and the latest version of the desktop suite is called Office 2019. Microsoft would much rather you bought the subscription, not only because it delivers recurring revenue, but also because Office 365 is a great upselling opportunity. Once you are on Office 365 and Azure Active Directory, products like Dynamics 365 are a natural fit.

Microsoft’s enthusiasm for the subscription product has resulted in a recent “Twins Challenge” campaign which features videos of identical twins trying the same task in both Office 365 and Office 2019. They are silly videos and do a poor job of selling the Office 365 features. For example, in one video the task is to “fill out a spreadsheet with data about all 50 states” (US centric or what?).

image

In the video, the Office 365 guy is done in seconds thanks to Excel Data Types, a new feature which uses online data from the Bing search engine to provide intelligent features like entering population, capital city and so on. It seems though that the twins were pre-provided with a spreadsheet that had a list of the 50 states, as Excel cannot enter these automatically. And when I tried my own exercise with a few capital cities I found it frustrating because not much data was available, and the data is inconsistent so that one city has fields not available for another city. So my results were not that great.

image

I’m also troubled to see data like population chucked into a spreadsheet with no information on its source or scope. Is that Greater London (technically a county) or something less than that? What year? Whose survey? These things matter.

Perhaps even more to the point, this is not what most users do with Office. It varies of course; but a lot of people type documents and do simple spreadsheets that do not stress the product. They care about things like will it print correctly, and if I email it, will the recipient be able to read it OK. Office to be fair is good in both respects, but Microsoft often struggles to bring new features to Office that matter to a large proportion of users (though every feature matters to someone).

It is interesting to browse through the new features in Office 2019, listed here. LaTeX equation support, nice. And a third time zone in Outlook, handy if you discover it in the convoluted Outlook UI (and yes, discoverability is a problem):

image

It is worth noting though that for document editing the free LibreOffice is excellent and good enough for a lot of purposes. You do not get Outlook though, and Calc is no Excel. If you mostly do word processing though, do look at LibreOffice, it is better in some respects than Word (style support, for example).

I use Office constantly and like all users, I do have a list of things I would like fixed or improved, that for the most part seem to be completely different from what the Office team focuses on. There are even longstanding bugs – see the recent comment. Ever had an email in Outlook, clicked Reply, and found that the the formatting and background of the original message affects your reply text as well and the only way to fix it is to remove all formatting? Or been frustrated that Outlook makes it so hard to make interline comments in a reply with sensible formatting? Or been driven crazy by Word paragraph numbering and indentation when you want to have more than one paragraph within the same numbered point? Little things; but they could be better.

Then again there is Autosave (note quite different from autorecover), which is both recent and a fantastic feature. Unfortunately it only works with OneDrive. The value of this feature was brought home to me by an anecdote: a teenager who lost all the work in their Word document because they had not previously encountered a Save button (Google docs save automatically). This becomes what you expect.

So yes, Office does improve, and for what you get it is great value. Will Office 2019 users miss lots of core features? No. In most cases though, the Office 365 subscription is much better value.

Which application platform for desktop Windows apps? Microsoft has stated its official line, but UWP is still not compelling

One year ago I wrote a post on Which .NET framework for Windows: UWP, WPF or Windows Forms? which is still the most popular post on this site, indicating perhaps that this is a tricky issue for many developers. That this is a live question is a symptom of Microsoft’s many changes of strategic direction over the last decade, making it hard for even the most loyal developers to read the signals.

I was intrigued therefore to note that Microsoft has an official Choose your platform post on this subject. There is something curious about this post. It covers three frameworks: Universal Windows Platform (UWP), Windows Presentation Foundation (WPF) and Windows Forms (WinForms). Microsoft states:

UWP is our newest, leading-edge application platform.

implying that if you have an unconstrained choice, this is the way to go. Yet if you look at the table of “Scenarios that have limited support”, UWP has the longest list. It is not only Windows 7 support that you will miss, but also something called Dense UI, along with other rather significant features like multiple windows and “full platform support”.

What is Dense UI? I presume this is a reference to the chunkiness of a typical UWP UI, caused by the fact that it was originally optimised for touch control. This matters if, for example, you are writing a business application and want to have a lot of information to hand in a single window. It may not be ideal for cosmetics, but it can be good for productivity.

With respect to all three of these limitations, Microsoft does note that “We have publicly announced features that will address this scenario in a future release of Windows 10.” I am not sure that they are in fact fully addressed; but it is clear that improvements are coming. In fact, the promise of further active development is perhaps the key reason why you might choose UWP for a new project, that is, if you do not learn from the past and believe that UWP will still be core to Microsoft’s strategy in say five years time.

Take a look at the strengths column for UWP though. Anything really compelling there? To my mind, just one. “Secure execution via application containers.” Yet the security of UWP was undermined by Microsoft’s decision to abandon its original goal of restricting the Windows Runtime API (used for UWP) to a safe subset of the full Windows API. You can also now wrap WPF and WinForm applications using Desktop Bridge, getting Store delivery and a certain amount of isolation.

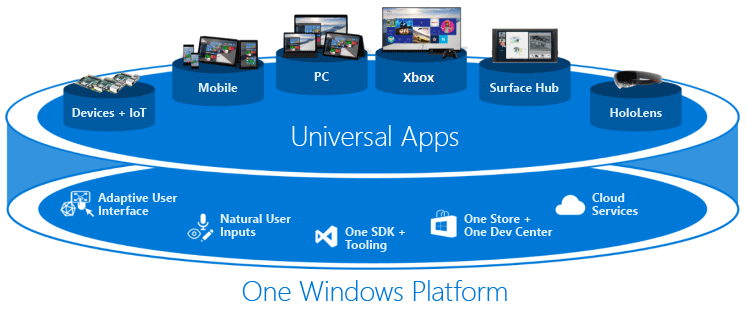
At the time of writing, Microsoft is still displaying this diagram in its guide to UWP.

image

This is now somewhat misleading though. Windows Mobile is on death row:

Windows 10 Mobile, version 1709 (released October 2017) is the last release of Windows 10 Mobile and Microsoft will end support on December 10, 2019. The end of support date applies to all Windows 10 Mobile products, including Windows 10 Mobile and Windows 10 Mobile Enterprise.

Windows 10 Mobile users will no longer be eligible to receive new security updates, non-security hotfixes, free assisted support options or online technical content updates from Microsoft for free.

As a developer then, would you rather have PC, Xbox and HoloLens support? Or PC, Mac, iOS and Android support? If the latter, you would be better off investigating Microsoft’s Xamarin Forms framework than UWP as such.

The truth is, many developers who target Windows desktop applications do so because they want to run well on Windows and are not concerned about cross-platform. While that may seem odd from a consumer perspective, it is not so odd for corporate development with deskbound users performing specific business operations.

I was at one time enthusiastic about Windows Runtime/UWP because I liked the idea of “one Windows platform” as illustrated above, and I liked the idea of making Windows a platform for secure applications. Both these concepts have been thoroughly undermined, and I would suggest that the average developer is probably better off with WPF or WinForms (or other approaches to Win32 applications such as Delphi etc), than with UWP. Or with Xamarin for a cross-platform solution. That is unfortunate because it implies that the application platform Microsoft is investing in most is at odds with what developers need.

If UWP becomes a better platform than WPF or WinForms in all important respects, that advice will change; but right now it is not all that compelling.

Microsoft quarterly financials: strong figures, note LinkedIn and Dynamics numbers

Microsoft has released its financial statements for the quarter ending December 31 2018. Sometimes it seems that all the talk is of Google, Facebook, Apple and Amazon, but Microsoft continues to deliver strong results.

That said, it is an increasingly corporate story. The company still has a presence in gaming, both on Xbox and PC, and reports Xbox software and services growth of 31%. Consumers still buy Windows and Office; there are now 33.3 million Office 365 consumer customers.

There is no longer a PC in every home though. There might be an old one; but PCs now  tend to be bought for specific purposes such as gaming or home working. There are plenty of other options for casual home computing. Windows OEM revenue is down 5%.

It is a different story in the business world. Office 365 is still motoring, with revenue growth of 34% year on year. A spin-off benefit is that Dynamics 365, once a poor cousin to Salesforce for cloud CRM, now reports revenue growth of 51% year on year, despite the product’s eccentricities and high price. The key is integration and upsell: get users hooked on Office 365 for email and documents, and compelling add-ons become an easy sell.

Rather to my surprise, Microsoft’s LinkedIn acquisition seems to be working. Revenue is up 29%, session numbers are up 30%. My anecdotal experience bears this out. People are actually acquiring and doing business via LinkedIn, even though it suffers from masses of bad data and the usual perils of social media (fake accounts, scammers, harassers and so on). For now, users seem to be able to manage these problems and interact with the right people.

Azure revenue is up 76%.

All well in Redmond then? The risk is that the company’s narrowing focus will leave it vulnerable to competitors who take advantage of their control of the end points (clients): smartphones, tablets, smart devices running Linux. Even now the web browser, with the Edge team now integrating Google’s browser engine, Chromium, rather than building their own.

For now though, Microsoft powers on.

Here is the breakdown by segment, such as it is:   

Quarter ending December 31st 2018 vs quarter ending December 31st 2017, $millions

Segment Revenue Change Operating income Change
Productivity and Business Processes 10100 +1147 4015 +678
Intelligent Cloud 9378 +1583 3279 +447
More Personal Computing 12993 +823 2964 +454

The segments break down as:

Productivity and Business Processes: Office, Office 365, Dynamics 365 and on-premises Dynamics, LinkedIn

Intelligent Cloud: Server products, Azure cloud services

More Personal Computing: Consumer including Windows, Xbox; Bing search; Surface hardware